
Rolling Out MFA Without Locking Out Your Team
MFA reduces the risk that a stolen password alone grants access, but a rushed rollout can strand employees or leave bypass paths unmanaged. Start with the identities that carry the highest business impact.

On this page
What this addresses
MFA reduces the risk that a stolen password alone grants access, but a rushed rollout can strand employees or leave bypass paths unmanaged. Start with the identities that carry the highest business impact.
Practical implementation steps
- Classify accounts by privilege and service criticality
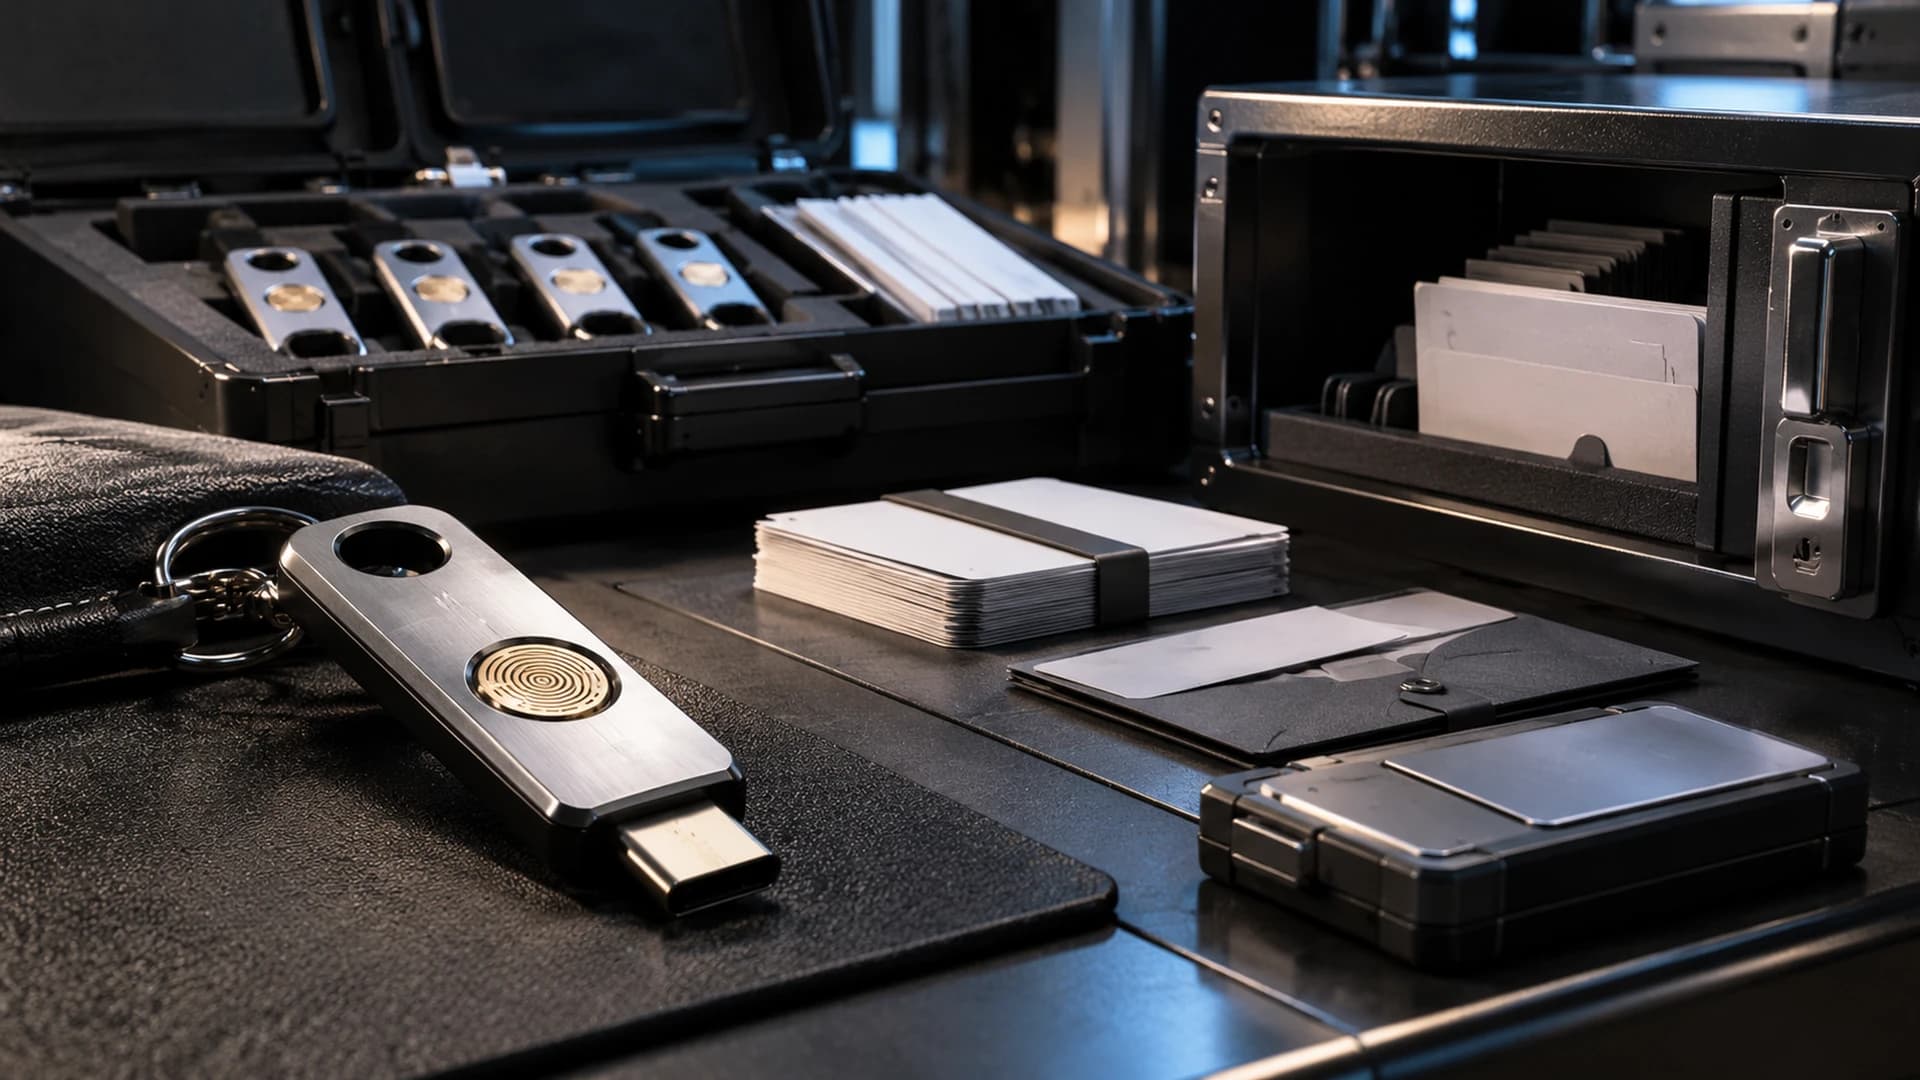
- Select phishing-resistant factors where supported
- Pilot enrollment with a small representative group
- Provide controlled recovery and replacement-device procedures
- Monitor enrollment completion and legacy login bypasses
Acceptance test
Test normal login, lost-device recovery, suspended employee access and a failed second-factor attempt before expanding the rollout.
Common failure mode
SMS-only coverage or a help desk that resets factors without identity verification can undermine the investment.
Separate enrollment from enforcement
Publishing an enrollment link is not the same as requiring a second factor. Inventory interactive login paths, mobile clients, administrator consoles and recovery mechanisms before choosing enforcement rules. Assign an owner to identities that cannot use the standard factor, such as an unattended integration. Do not enroll a machine identity as though it were a person sharing a phone. A deployment plan should name the scope, supported factors, help channel, pilot group and criteria for moving each group to enforced protection.
Prefer stronger factors where the service supports them
Phishing-resistant authenticators can prevent some attacks that relay passwords and one-time codes, but their availability and recovery behavior differ between providers. Check the exact product documentation and test the real sign-in flow rather than treating every product labeled MFA as equivalent. Authenticator apps can still improve a password-only system when stronger options are unavailable. Keep a documented exception plan for users who cannot use the standard method; exclusions should have an owner and review date, not silently remain permanent.
Pilot the uncomfortable cases
Use a small group representing remote staff, shared workstations, accessibility requirements and privileged users. Test a replacement phone, lost authenticator, expired session, employee departure and a legitimate login from a new device. Include the person who supports users after hours. Observe whether recovery grants a normal session, resets the factor or requires a separate authorization; these are different outcomes. Record clear instructions in language the user understands and verify they can recover without asking colleagues to share credentials.
Treat the help desk as part of authentication
An attacker may bypass a strong factor by persuading support to reset it. Define evidence for identity verification and escalation, and ensure a single unverified call cannot reset a high-impact administrator account. Notify the account holder through an established channel after factor changes and make the event visible to security staff. Recovery codes must be stored securely and consumed once. Do not ask employees to send codes or screenshots of authenticator seeds to a shared mailbox as proof of enrollment.
Roll out in waves and prove coverage
Move a bounded group from enrollment to enforcement only after support and recovery work. Monitor blocked legacy paths, failed enrollment, suspicious repeated prompts and exceptions. Unexpected failures require investigation; a broad global exclusion can restore an attacker’s password-only path. Measure protected interactive identities against the actual in-scope population, including administrators and contractors. The exit criteria are a verified protected login, denial when the factor is absent, controlled recovery and timely revocation. Keep a rehearsed, tightly controlled emergency access procedure so that a provider outage does not force an improvised security rollback.
Primary references and further reading
Connect the idea to your business.
Start with your goals, existing systems and constraints before choosing a solution.
IT Services